How do you turn your employees into a ‘human firewall’? Sophos Phish Threat has the answer, as we look at a mind-boggling example of how phishing emails caused disastrous consequences for a global organisation in the movie industry.
As outlined by global cybersecurity experts Sophos, phishing is a type of cyberattack where attackers send fraudulent messages designed to trick people into revealing sensitive information or downloading malicious software.
These deceptive communications often impersonate trusted organisations like banks, utilities or work colleagues. It’s one of the most common and dangerous methods threat actors use to compromise security defences.
Sony Pictures discovered this to their cost when, in one of those ‘Truth is stranger than fiction’ moments, they were ‘phished’ and realised that they could not have imagined writing a worse script for themselves.
Straight From the Movies, Except It Was Real Life
In 2014, Sony Pictures suffered a frightening cyberattack that cost the company tens of millions of dollars (as a conservative estimate).
Attackers sent phishing emails in October of that year, disguised as Apple ID verification requests to Sony executives:
There have been reports of unauthorized activity on your Apple account. Verify your Apple ID to secure your account.
When nervous employees responded to this warning and gave their credentials, the threat actors got in and harvested information, to then re-use across Sony’s network.
Although nothing overtly consequential happened at the time, it was to become one of the most damaging corporate breaches on record.
The following month, on 24 November 2014, employees at Sony Pictures turned on their computers to find that the ‘Guardians of Peace’ – a group of cybercriminals assumed to have links with North Korea (more on this later) – had taken over their network. The attackers had taken terabytes of private data, deleted the original copies from Sony computers, and left messages threatening to release the information if Sony didn’t comply with the attackers’ demands.
And they proceeded to carry out their threat.
Confidential emails, executive communications and employee data were leaked, as well as unreleased films still in the pipeline. As well as suffering huge embarrassment, the company also lost millions of dollars in revenue.
But why was Sony Pictures targeted like this in the first place?
The catalyst for the anger shown by the ‘Guardians of Peace’ turned out to be Sony Pictures’ latest comedy scheduled for imminent release, entitled ‘The Interview’, which was a satirical political action-comedy starring James Franco and Seth Rogen, who was also a director.
Editor’s note: Just the name ‘Seth Rogen’, one of Hollywood’s most famous anti-establishment actor-directors, offered a premonition of irreverence in the mix, especially when teamed with his sidekick James Franco: their reputations already preceded them. The movie featured fictional engagement with the real-life leader of North Korea, and this information made its way to that country before the movie was released. The concept went down like a lead balloon, and in June 2014, the North Korean government formally complained to the United Nations.
Without actually naming the movie specifically, but including enough confirmed details such as naming the two main actors and outlining the basic plot, the complaint labelled the film an ‘act of war’ and state-sponsored terrorism, and threatened ‘a firm and merciless response’. Joining the dots, it would be a reasonable assumption to assume that the ‘Guardians of the Peace’ were then hired by the North Korean government.
The threat actors demanded that Sony ‘stop immediately showing the movie of terrorism’ and threatened cinema-goers with a ‘bitter fate’ if the movie was shown widely in cinemas as planned. As a result, Sony decided to pull the movie before its global release to cinema franchises.
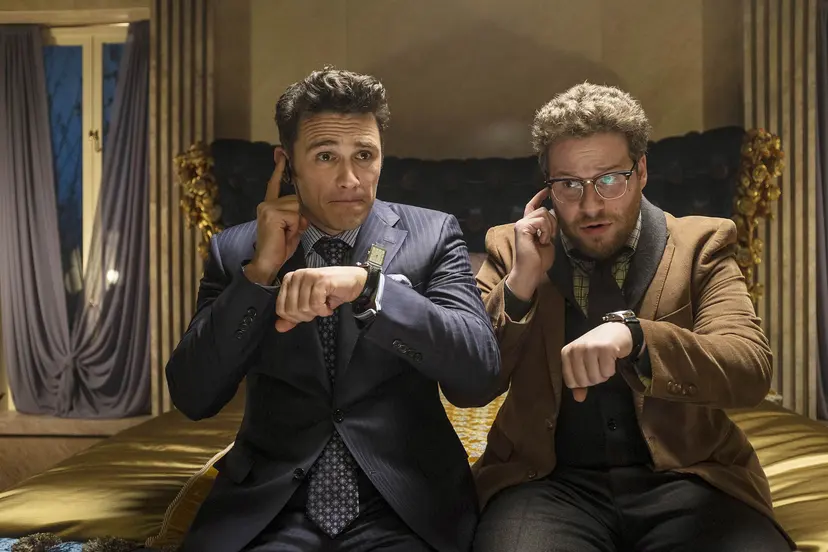
Instead, ‘The Interview’ was eventually released only to online platforms and a limited number of independent cinemas, after critics argued against giving in completely to the hackers.
The net result: a film that took $44 million to make, and which was flagged to make Sony a good deal of money, eventually grossed only $12.3 million in box office sales worldwide – although it did eventually make around $40 million in digital rentals, to become Sony’s biggest digital release at the time.
Back to the cyberattack.
Having tailored the fake emails to Sony’s employees in such a way as to generate anxiety, the threat actors prompted the employees to follow a link and complete a fake verification form. Once the hackers had these details, they used that information to hack into their Sony accounts. After this, it was an easy step to cripple Sony’s network with a strain of malware called ‘Wiper’.
For a company in the business of making movies, the script was one of those ‘Truth is stranger than fiction’ scenarios – in the worst possible way.
It’s a sobering story, but one that arguably could have been prevented if Sony’s employees had been more aware of criminal tendencies, and less frightened of the alleged prospects of being locked out of their Apple accounts.
But of course we will never know that, with hindsight being, as the saying goes, ‘20-20 vision’.
Why People-First Security Matters
Technology stops a huge number of threats, but the single biggest risk to most organisations remains the end user. The Sony warning story reminds us firsthand how the attack began with malevolent emails, after which unwitting click-throughs led to compromised credentials and the secretive deposit of crippling malware on the system.
Sophos Phish Threat aims to elevate employees from being the problem to a valued part of the defensive fabric by creating repeatable, safe practice through simulation and education.
Sophos Phish Threat is a full security-awareness programme that tests employees with realistic phishing simulations and immediately delivers targeted, bite-sized training to anyone who takes the bait and clicks.
The result is measurable behaviour change, better reporting and a genuinely smaller human attack surface for your organisation.
Typical use cases could include the following:
- Finance teams: Realistic invoice and payment-fraud simulations teach employees to pause and verify before acting on payment requests.
- Healthcare: Protect patient data with role-based campaigns for clinical and admin employees who handle sensitive records.
- Legal and professional services: Train employees to spot partner impersonation and other social-engineering lures.
Sophos is a recognised leader in endpoint and network security solutions, while Vox is an accredited Sophos Platinum partner and is certified to implement, manage and support Sophos solutions across the product stack. We offer local, South African-based support with business-focused service levels.
And so our best-practice advice is as follows: Activate your human firewall today!
Don’t let your company become the main punchline of another hideous set of media headlines.
Talk to your Vox Business account manager for a tailored quote and a recommended pilot that reflects your industry risk profile.
Contact: +27 (0) 87 805 0500, or email: info@voxtelecom.co.za
Frequently Asked Questionss
What is Sophos Phish Threat?
Sophos Phish Threat is a cloud-based security awareness platform that runs realistic phishing simulations and delivers automated, on-the-spot training to anyone who fails a simulated attack. It helps organisations reduce phishing susceptibility and build a human firewall.
How does the training get delivered?
Anyone who clicks in a simulated phishing campaign is automatically enrolled in a short, interactive training module relevant to the lure. Training is delivered immediately to reinforce learning at the moment of error.
Can Sophos Phish Threat be customised for my industry?
Yes. The platform offers a custom campaign builder and industry-relevant templates so you can tailor campaigns and training modules to specific teams, departments or threat profiles.
How is success measured?
Success is measured through dashboard KPIs, including click rates, report rates, training completion and trend analysis over time, which show reductions in employee susceptibility and improvements in reporting behaviour.
About Author